PHP developers release fixes for two critical flaws after government websites go offline
PHP developers have released four security patches and urged immediate updates, while the PHP Foundation acknowledged a failure in handling an earlier warning.
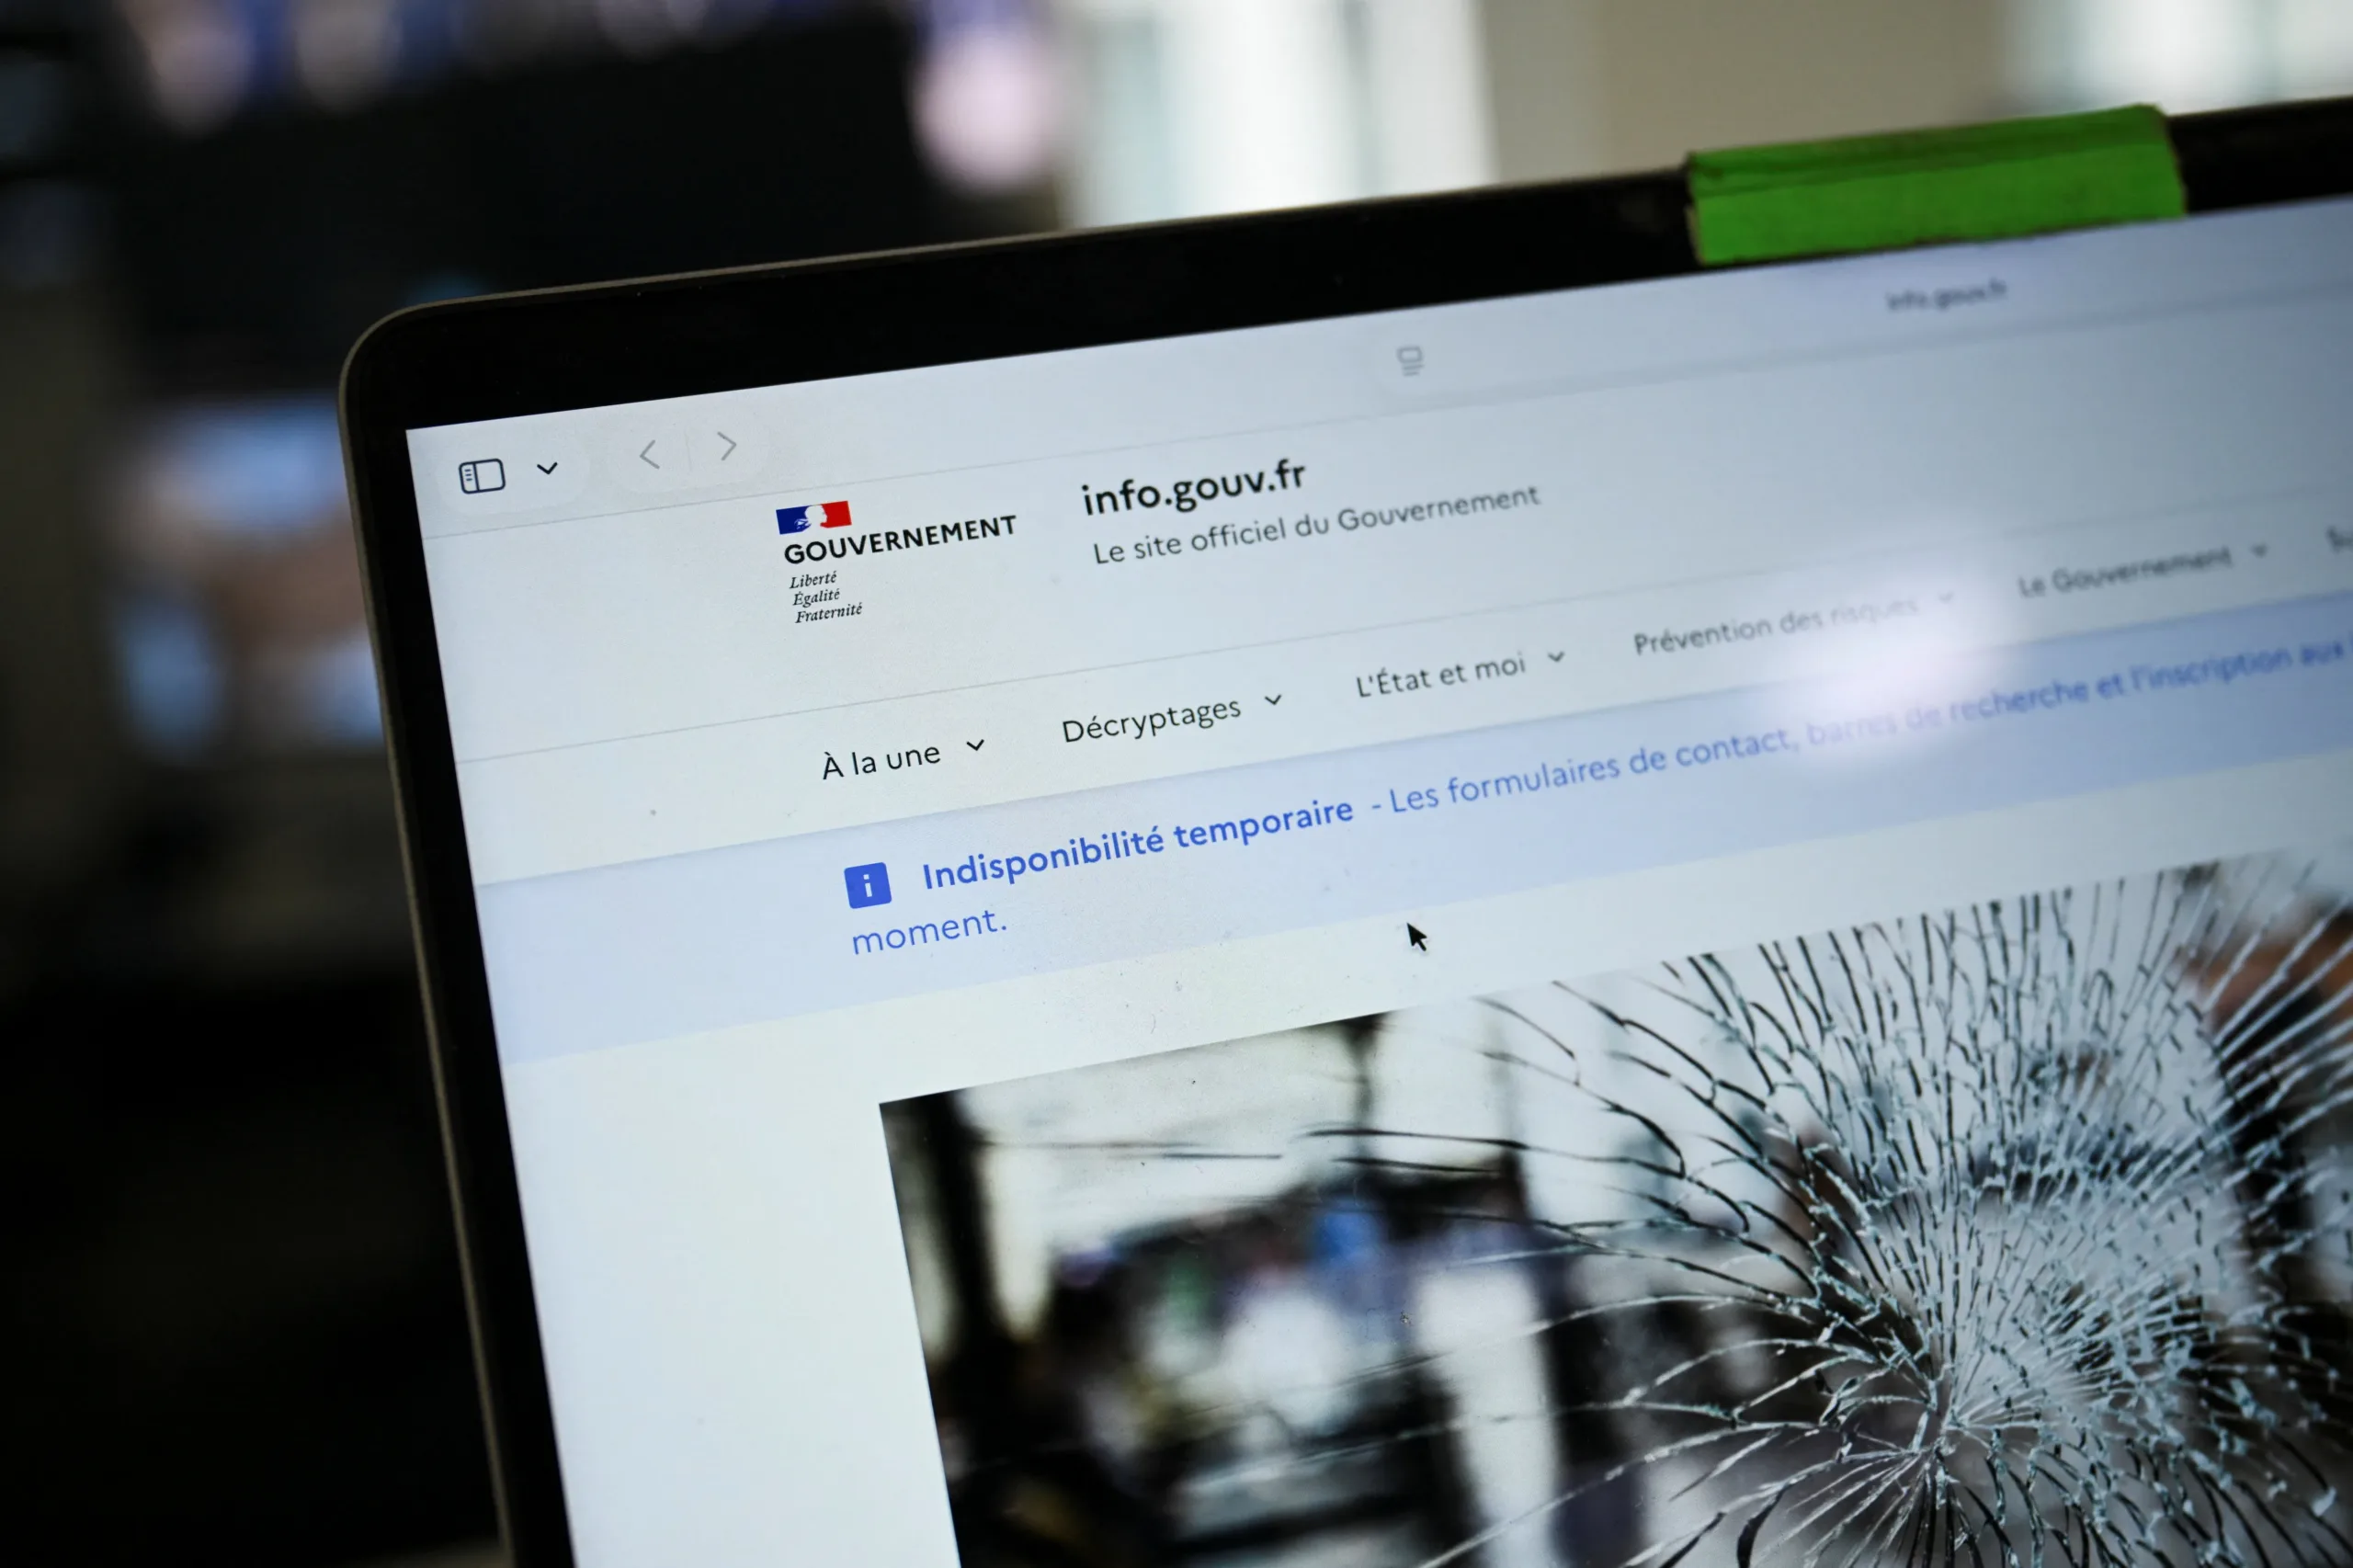
Washington, United States. PHP developers have made four patches available to fix two previously identified critical security vulnerabilities, urging users to install updates immediately. Government websites across Europe and other regions went offline on Wednesday as operators worldwide rushed to secure their systems following disclosure of the flaws.
Critical flaws prompt urgent update calls
The vulnerabilities could enable hackers to run code on affected systems, according to the developers. Because PHP supports a substantial share of internet infrastructure, the disclosure raised concerns about the potential exposure of many websites.
Before releasing the fixes, the developers had announced the discovery of two critical vulnerabilities and advised users to update their websites once patches became available. Security specialists warned that attackers would rapidly analyse the fixes to identify ways of exploiting systems that remained unpatched.
Foundation acknowledges delayed response
In a blog post, the PHP Foundation, which supervises the software’s development and upkeep, acknowledged that an earlier warning had not been addressed promptly.
The foundation said a security researcher had detected initial indications of a flaw in 2024 that subsequently led to one of the vulnerabilities. It explained that the concern had remained theoretical because no concrete attack methods had been identified, while other clearly established problems with demonstrable consequences had taken priority.
The foundation characterised the delay as a structural failure.
US agencies issue security advice
The US National Security Agency said the vulnerabilities could often give attackers direct access to a server’s file system or database. It advised organisations unable to update immediately to disconnect affected systems to fully mitigate the risk.
In a separate advisory, the Cybersecurity and Infrastructure Security Agency (CISA) called for organisations to update their PHP installations without delay. CISA said it had seen no exploitation of the vulnerabilities when its advisory was published, but warned that organisations leaving systems unpatched would remain at risk.
This news item was generated automatically by Cyprus Inform from publicly available materials. Report an error →